CISO / Risk Leader
Enforceable least privilege, a smaller blast radius, and evidence that each control is operating.
Security stacks grow one product at a time, and after a few years no single team owns the whole control path. ModernOps designs the layers as one system, starting with identity, then the devices, applications, data and network edge that depend on it.
Enforceable least privilege, a smaller blast radius, and evidence that each control is operating.
One accountable partner across architecture, procurement, implementation and operations.
A governed edge: documented rulebases, validated HA, ticketed changes and monitoring on the firewalls, VPNs and NAC your users depend on.
A phased path from AD, GPO and legacy authentication to Entra, Intune and Conditional Access, without breaking what still depends on the old world.
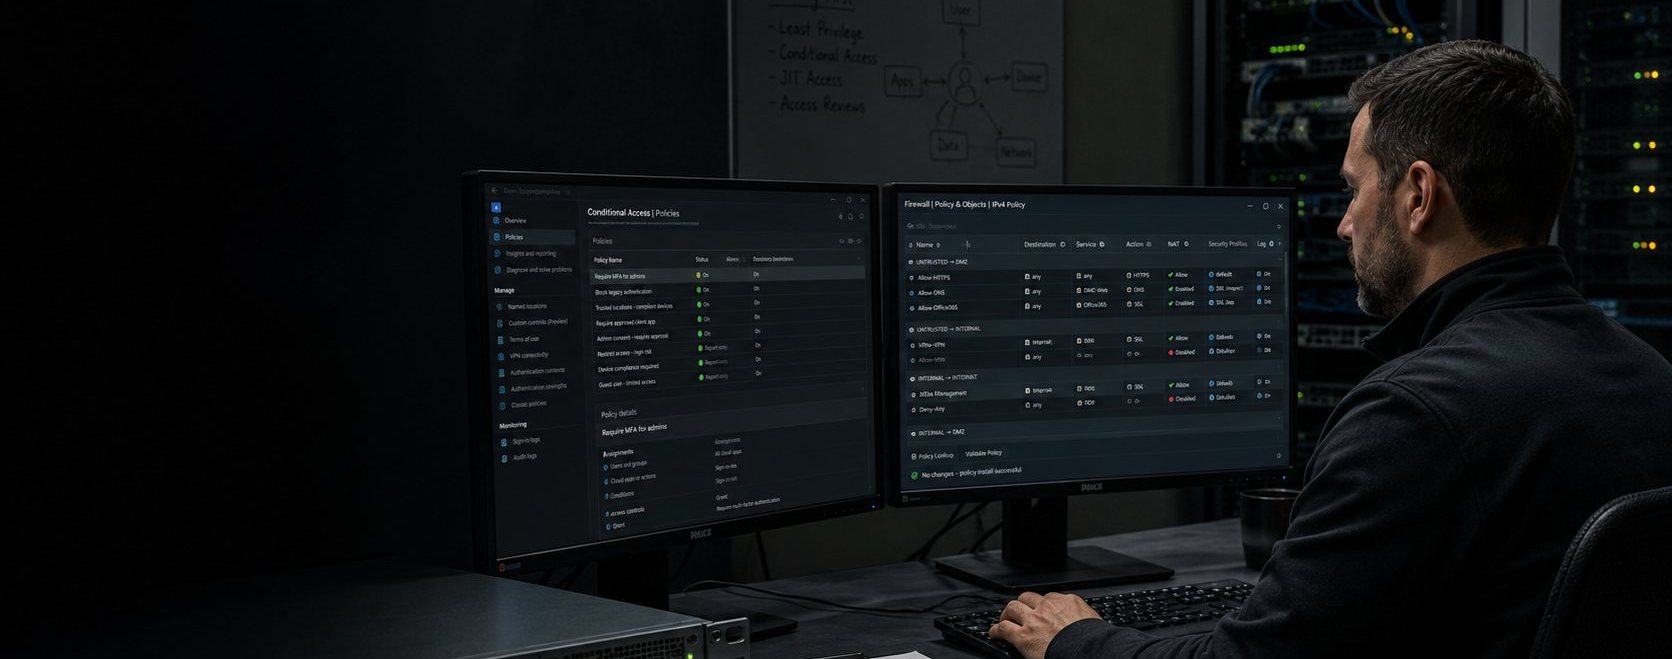
Licensing MFA and enforcing least privilege are different projects. One recent assessment found MFA unenforced, no Conditional Access, and administrator accounts doubling as daily-use accounts. The remediation was structural: separated privileged roles, Conditional Access, just-in-time elevation and access reviews.
A firewall doing decryption, IPS and application control delivers a fraction of its datasheet rating. Firewalls sized to the headline figure tend to run out of capacity in year two, so we size against measured throughput with inspection enabled.
In the tenants we review, E5 and P2 entitlements such as Conditional Access, PIM, Defender and Purview often sit unconfigured while point products are bought to do the same jobs. Activating what you already license is usually the cheapest security project available.
LDAP, NTLM, Kerberos, GPO, service accounts and aging applications hang off Active Directory. Leaving AD means mapping those dependencies, remediating them in phases, and keeping hybrid only where a dependency justifies it.
Fewer consoles means fewer missed alerts; the tradeoff is less room to negotiate. Either answer can be defended, and in our experience security renewals carry more pricing flexibility than any other line on the renewal pile.
Legacy ASA-class estates moved to Palo Alto or Fortinet: rule rationalization, NAT and VPN documentation, policy conversion, HA validation and staged cutover, delivered as a productized service we have run many times.
FortiGate-class firewalls for branch and mid-market sites where price-performance decides, sized with inspection enabled and onboarded with the rulebase archived and changes ticketed from day one.
Entra-first target states built on a mapped current state: Conditional Access, MFA enforcement, PIM, access reviews and entitlement management, with a dependency-aware, phased reduction of on-premises AD. Delivered through structured engagements up to full identity and access strategy workshops.
Intune and Autopilot deployment, Defender for Endpoint, encryption, attack surface reduction and BYOD application protection, including migrations from ConfigMgr, Jamf, Workspace ONE and MobileIron, so device health becomes an input to every access decision.
Zscaler policy and tenant operations, Microsoft Global Secure Access evaluation, Duo MFA lifecycle, and network access control with Cisco ISE and Aruba ClearPass, designed jointly with the switching practice so segmentation intent survives into the network.
SaaS discovery and app-consent governance with Defender for Cloud Apps, data classification and DLP with Purview, and integration patterns like Rubrik with Okta, where sensitive-data access risk can force reauthentication or kill a session automatically. The design goal is detection that ends in an automated action rather than a ticket.
NGFW hardware from branch to data center, subscription structuring and renewals, and the migration practice that moves aging estates onto the platform. Because we also quote Fortinet, Palo Alto renewals are negotiated with a priced alternative on the table.
The FortiGate line from 70G-class branch boxes to enterprise chassis, FortiGuard services, and the price-performance play, quoted with inspection-on throughput instead of datasheet numbers, and operable under managed firewall service from day one.
Falcon licensing, renewals and endpoint standardization for teams committed to best-of-breed EDR, paired with Managed Security for organizations without a SOC.
Cloudflare One as the Zero Trust edge: Access in front of internal applications, Gateway for DNS and web filtering with DLP on what leaves the browser, and the WARP client for device posture, tied to Entra or Okta identity. On the network side, DDoS protection and authoritative DNS where the internet edge belongs in the security design. Specified, deployed and operated alongside the firewall and identity work on this page.
The stack many organizations already license and underuse: Entra Conditional Access and PIM, Intune and Autopilot, the Defender family, Sentinel and Purview, delivered by a senior-led practice through assessments, workshops, implementations and migrations. Our standing advice is to activate the tools inside your E5 before buying the next one.
Zscaler tenant and policy management, Microsoft Global Secure Access design, Duo MFA lifecycle operations, and NAC with Cisco ISE and Aruba ClearPass, including posture policy, directory and MDM integration and HA validation.
Cisco Secure (Firepower, Umbrella, Meraki MX), Okta, Proofpoint, Arctic Wolf, SentinelOne, KnowBe4, Varonis, Delinea, Wiz.
| Dimension | The old model | ModernOps |
|---|---|---|
| Architecture | Firewall, endpoint, identity and data controls bought separately | One Zero Trust system across identity, devices, applications, data and the edge |
| Identity | MFA inconsistent, admin and daily accounts overlap | Enforced MFA, Conditional Access, separated privileged roles, PIM, access reviews |
| Firewall operations | Rules, NAT and VPNs are undocumented | Rulebase archived, objects documented, HA validated, changes ticketed |
| Device trust | Unknown devices reach company data | Compliance, encryption and Defender posture gate access, BYOD contained by policy |
| Applications | Users grant consent, shadow SaaS accumulates | App discovery, consent governance and session controls shrink the exposure |
| Data | Policy watches where data sits and misses where it moves | Classification, labels and DLP follow the data across endpoints and SaaS |
| Ownership | Reseller, implementer, MSP and vendors point at each other | One team architects, sources, deploys, operates and escalates |
| Phase | What happens | What you hold at the end |
|---|---|---|
| Assess · Days 1 to 7 | Inventory firewalls, ZTNA, identity providers, privileged roles, endpoints, app consent, data controls, licensing and legacy dependencies. Review rulebases, MFA and Conditional Access coverage and incident workflows. | A fact-based baseline: immediate exposure, unused entitlements you already pay for, and prioritized quick wins. |
| Implement · Days 8 to 21 | Archive configurations, separate privileged accounts, enforce MFA, restrict app consent, land approved Conditional Access, firewall, endpoint and data policies, connect monitoring, pilot the high-impact changes first. | The highest-risk exposures closed under change control, with testing, documentation and rollback. |
| Optimize · Days 22 to 30 | Tune alerts and policies, validate HA and access paths, review exceptions, finalize ownership and change workflows, train administrators. | Measurable controls in production, documented baselines, named ownership and a 30-to-90-day roadmap. |
Thirty days lands the baseline and the quick wins. Full identity migrations and firewall estate cutovers then run in dependency-aware phases on their own timeline, which is what exiting twenty years of Active Directory requires.
This page is the assess, design, procure, implement and migrate motion. The recurring disciplines are productized: Managed Security carries firewall policy operations, monitoring, endpoint and identity administration and coordinated response, and it works on estates we sold or estates we inherited. Device lifecycle lives with the Microsoft practice.
A global software company commissioned a forty-hour identity and access strategy engagement covering Conditional Access, Global Secure Access, device strategy and E5 utilization, with Zero Trust planned as a multi-quarter program.
MFA unenforced, no Conditional Access, admin accounts doubling as daily accounts, unmanaged devices and untracked third-party app consent. The roadmap closed them in phases, starting with the free fixes.
ModernOps runs its own operations the way this page prescribes: Entra-authenticated, MFA-enforced, encrypted administrative access and separated privileged roles.
Firewalls, identity, endpoints: whatever you have. We will map the exposure and the entitlements you already own.